GitHub Copilot Autofix logo
AI Code Review FREE TRIAL from $30/mo

GitHub Copilot Autofix

It reviews vulnerabilities found in code and proposes automated fixes directly in GitHub, so developers can write secure code at scale instead of leaving security tickets in a backlog.

GitHub Copilot Autofix is the AI-driven remediation feature in GitHub's application security offering. It reviews vulnerabilities found in code and proposes automated fixes directly in GitHub, so developers can write…

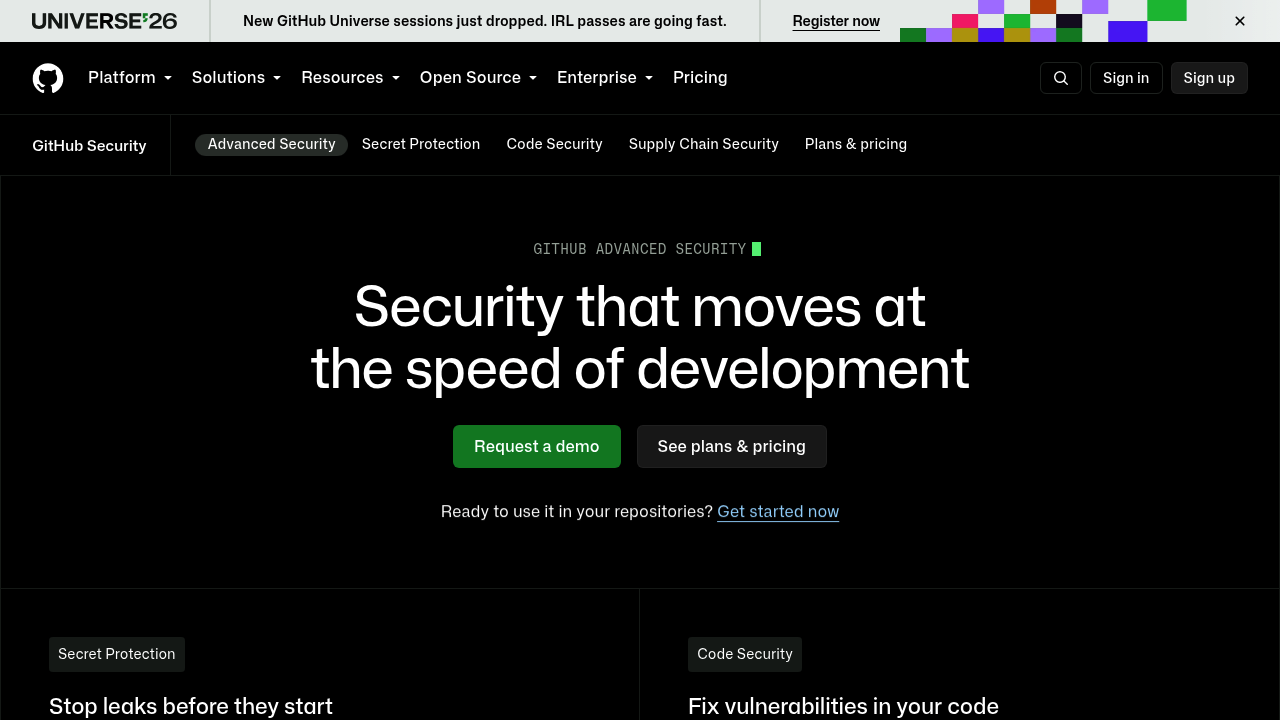
GitHub Copilot Autofix screenshot

GitHub Copilot Autofix is the AI-driven remediation feature in GitHub's application security offering. It reviews vulnerabilities found in code and proposes automated fixes directly in GitHub, so developers can write secure code at scale instead of leaving security tickets in a backlog. It belongs to GitHub Code Security, which is priced at $30 per active committer per month, while the companion GitHub Secret Protection product costs $19 per active committer per month.

GitHub Copilot Autofix targets development teams and organizations that already host their code on GitHub and want security built into the way they work. Application security teams gain time to focus on broader strategy when developers can resolve issues as they go, and engineering leaders at larger companies get a path to adopt security tooling without adding a separate workflow. Teams on Azure DevOps can also reach GitHub Advanced Security as an add-on.

In practice, a developer opens a pull request, the code is analyzed through static application security testing, and a suggested fix appears alongside the finding. Security engineers use the same environment for software composition analysis and secret scanning, which covers dependencies and leaked credentials in addition to flaws in the code itself. Organizations that want to evaluate the product can start with a 30-day GitHub trial that includes Enterprise and Advanced Security. Because everything runs inside the native workflows developers already know, adoption tends to depend on committer licensing rather than on training or new infrastructure.

GitHub Copilot Autofix alternatives

See all →

Frequently asked

6 questions
What does GitHub Copilot Autofix do?
AI-driven insights and automated fixes target vulnerabilities in your code. Suggestions appear within GitHub so developers can remediate problems during normal development.
Who should use GitHub Copilot Autofix?
Teams and organizations that host code on GitHub and are committed to fixing vulnerabilities before production are the intended audience. Security teams benefit as developers handle more remediation themselves.
How would a team apply GitHub Copilot Autofix day to day?
Code is analyzed with static application security testing inside GitHub, and fixes arrive alongside the findings. Developers review the proposal and merge it as part of the usual pull request flow.
How is GitHub Copilot Autofix priced?
Pricing comes through GitHub Code Security, which costs $30 per active committer per month. GitHub Secret Protection is a separate $19 per active committer per month, and a 30-day trial of GitHub Enterprise and Advanced Security is offered.
What are the limits of GitHub Copilot Autofix?
It is not sold on its own, since it comes inside the GitHub Code Security license that is billed per active committer. It also works within GitHub's native workflows, so its value depends on keeping your code there.
Does GitHub Copilot Autofix work with Azure DevOps?
GitHub Advanced Security is available as an add-on for Azure DevOps. Teams already on GitHub can enable it for repositories through the Code Security option.

Reviews (0)

Write review

No reviews yet. Be the first to share your experience.