
Free Wordfence Alternative — WordPress Security & Firewall Plugin
ShieldZip: a firewall that runs before WordPress, integrity-first malware scanning with no signature delays, 2FA, breached-password blocking, country blocking, live traffic and a local audit log — the features Wordfence sells for $149–$1,250/yr, free.
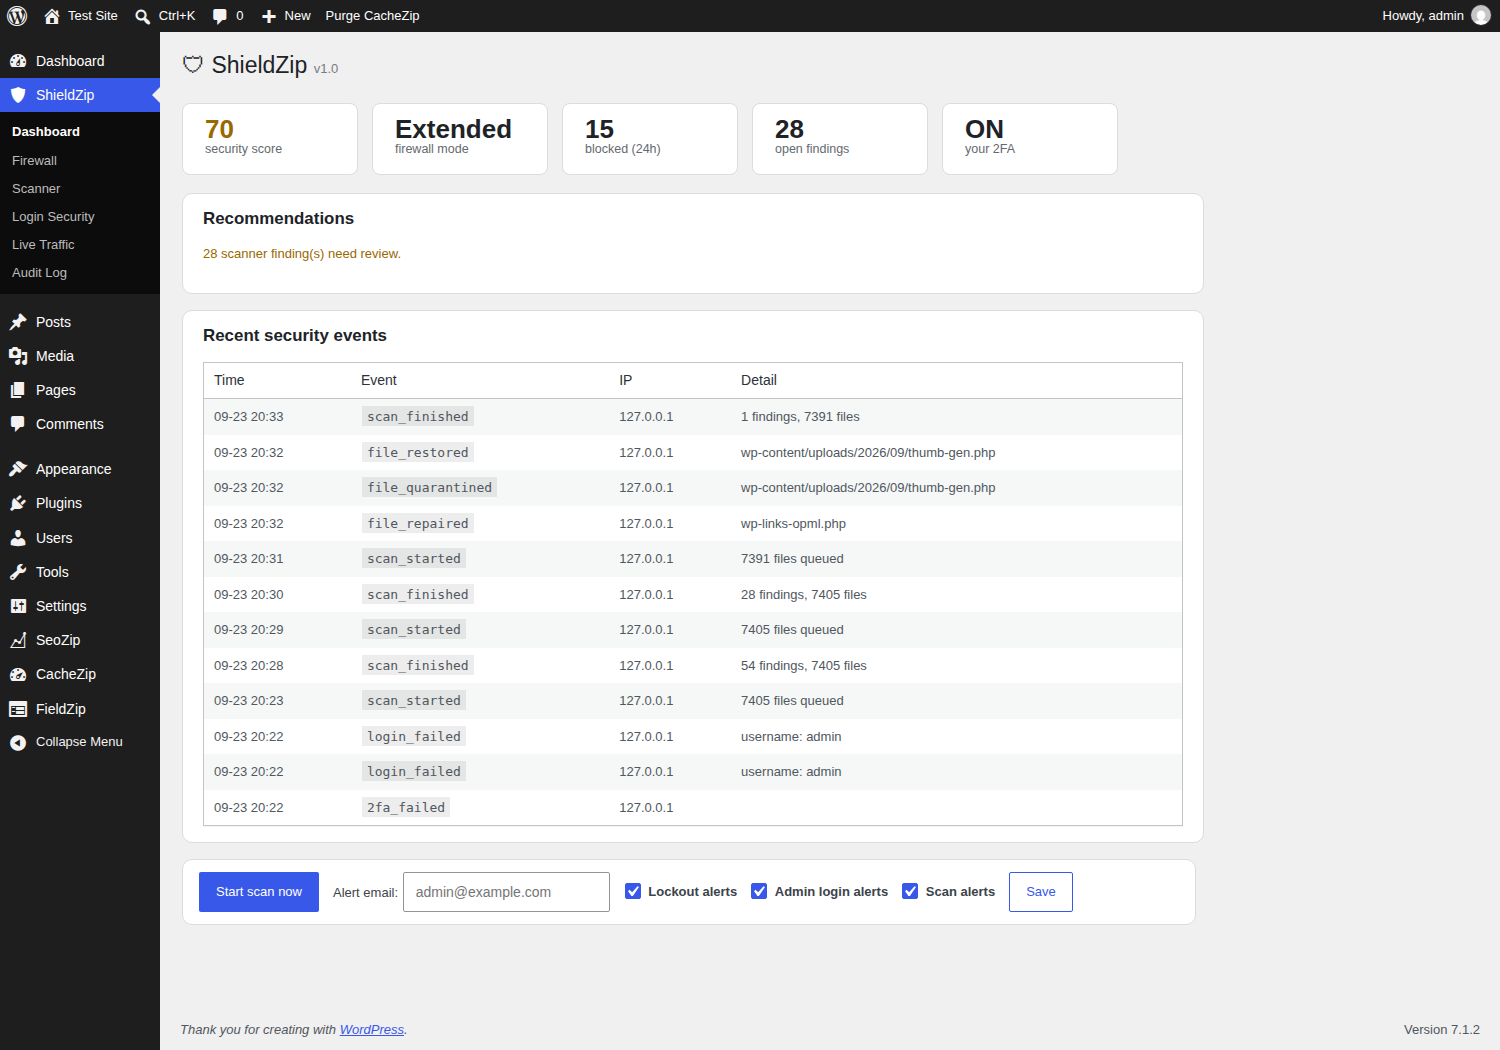
What it is
The firewall is the real thing, not a plugin-hook filter. One click installs PHP's auto_prepend_file (with reversible marker blocks in .htaccess and .user.ini, and a plugin-mode fallback for restrictive hosts), so SQL-injection, XSS, LFI and RCE rule families, IP blocks, rate limits and country blocking all execute before WordPress loads — and before any dropped rogue PHP file can run. In testing, a rogue file dropped into the web root was blocked without WordPress ever booting, and attacks aimed at cached pages were stopped before the page cache could even serve them — a request a plugin-phase firewall never sees. SQL-injection rules use a two-stage design (fast regex, then structural confirmation), so a search for "how to select a union" sails through while an actual injection is stopped.
The scanner inverts the signature-subscription model. WordPress core verifies against wordpress.org's own checksum API; plugins and themes verify against the exact-version packages from the official repository (premium packages are never falsely flagged); modified core files repair themselves from the source with one click, checksum-verified. On top: transparent obfuscation heuristics, an optional open GPL hash feed, database scanning (siteurl hijacks, obfuscated option values, external script injections in published posts — a layer the market leader doesn't have), rogue-admin detection via baseline diffing, publicly exposed backup/config detection, and vulnerability alerts from the free Wordfence Intelligence Community feed. Scans run in low-CPU background batches with a hash cache, so repeat scans read only changed files — a direct answer to the "security scan took the site down" genre of shared-hosting complaint.
Login security: TOTP two-factor implemented to RFC 6238 and verified locally with single-use replay protection and recovery codes; brute-force lockouts in a dedicated table with XML-RPC going through the same counters; masked login errors; and breached-password blocking via Have I Been Pwned's k-anonymity API — only the first five characters of a hash ever leave your server. Around it: a local audit log with unlimited retention, server-side live traffic with one-click blocking, four-channel username-enumeration protection, security headers, PHP-execution blocking in uploads, and a panic button that rotates your secret keys to kill every session. No accounts, no API keys, no phone-home.
ShieldZip vs Wordfence Security — feature by feature
Wordfence prices per site/year since Dec 2024: Premium $149 · Care $590 · Response $1,250. Wordfence Free ships the full engine but delays new firewall rules and malware signatures by 30 days — exactly the post-disclosure window when mass exploitation peaks. Rival free tiers gate harder: Solid Security is now inside $299/yr Kadence Pro, Sucuri's free plugin has no firewall at all.
| Feature | ShieldZip (free) | Wordfence |
|---|---|---|
| Firewall that runs BEFORE WordPress (auto_prepend_file) | ✓ one click, reversible marker blocks, plugin-mode fallback | Free ✓ (same mechanism) |
| Firewall rule freshness | Rules ship in the plugin — open source, no feed delay by design | Free: 30-DAY DELAY · real-time only with Premium $149/yr |
| Malware signature freshness | Integrity-first: wordpress.org checksums catch modified files with no signatures at all; heuristics + optional open GPL feed on top | Free: 30-day-old signatures · Premium $149/yr for real-time |
| Country blocking | ✓ free — IPv4 zones compiled to a binary-searched file, whole-site or login-only | Premium $149/yr |
| Scan scheduling control | ✓ | Premium $149/yr |
| Audit log | ✓ local database, unlimited retention | Free: preview only · 30/60/90-day retention at $149/$590/$1,250 — stored on their cloud |
| Database scanning (siteurl hijack, options, post injections) | ✓ | ✕ (documented gap — file scanning only) |
| Scanner that runs OUTSIDE the site's PHP process risk | Pre-WP firewall phase is independent of WP; scanner is batched, hash-cached, skips unchanged files (low CPU) | In-process; CPU/memory spikes on shared hosting are the #1 complaint |
| Core file repair from the official source | ✓ fetch + checksum-verify from wordpress.org SVN | Free ✓ |
| Plugin/theme integrity vs official packages | ✓ exact-version package manifests, premium packages never falsely flagged | Free ✓ (via their cloud copy) |
| Quarantine + restore | ✓ | Free ✓ (delete/repair) |
| Vulnerability alerts for installed plugins/themes | ✓ via the free Wordfence Intelligence Community feed (attributed) | Free ✓ |
| Two-factor authentication (TOTP) | ✓ RFC 6238, verified locally, single-use replay protection, recovery codes | Free ✓ |
| Breached-password login blocking | ✓ Have I Been Pwned k-anonymity, direct — 5 hash chars leave the server, padded responses | Free ✓ (proxied through Wordfence's servers) |
| Brute force lockouts (login + XML-RPC same counters) | ✓ dedicated table (object-cache safe), invalid-username insta-lock, masked errors | Free ✓ |
| Rate limiting + 404-storm auto-blocking | ✓ pre-WordPress, file-based counters | Free ✓ (plugin phase) |
| Username enumeration protection | ✓ all 4 channels: ?author=, REST /users, oEmbed, sitemap | Free ✓ |
| Live traffic (bots included) | ✓ server-side, one-click IP block | Free ✓ |
| Real-time IP reputation blocklist from a global network | — (by design: no telemetry network; local auto-blocks + your own lists) | Premium $149/yr |
| Works without any account or phone-home | ✓ zero registration; external calls only for features you invoke | ✕ even Free registers an API key and talks to their NOC servers |
| Hands-on cleanup service with SLA | — (it's software; the scanner + quarantine are the tools) | Care $590/yr · Response $1,250/yr (1-hour SLA) |
| Price | Free forever (MIT) | Free (delayed feeds) · $149–$1,250 per site per year |
Server requirements & dependencies
- WordPress 6.0 or newer (tested on WordPress 7.1)
- PHP 7.4 or newer
- wp-content must be writable (data directory + firewall stub)
- Optional: writable .htaccess/.user.ini for extended (pre-WordPress) protection — plugin mode works without it
- Nothing else: no accounts, no API keys, no subscriptions, no phone-home
How to install
2. ShieldZip → Firewall → "Enable extended protection". This installs auto_prepend_file (reversible marker blocks) so the firewall runs before WordPress — and before any dropped rogue PHP file. Note: PHP caches .user.ini for up to 5 minutes; the status turns green shortly.
3. ShieldZip → Scanner → "Start scan". It runs in low-CPU background batches; findings arrive with one-click actions: repair core files from wordpress.org, quarantine, ignore.
4. ShieldZip → Login Security: set up TOTP 2FA for your account (store the one-time recovery codes) and leave breached-password blocking on.
5. Optional: add country codes on the Firewall tab and click "Download & compile zone data"; add your alert email on the Dashboard.
Switching from another security plugin? Deactivate it first so two firewalls don't fight over auto_prepend_file.
The prompt — build it yourself
Paste this into Claude and you'll get this product. This is the actual spec that produced the code above.
Research phase: three parallel agents. The decisive findings: Wordfence's moat is not its PHP code but its feeds — free users get firewall rules and malware signatures 30 days late (precisely the mass-exploitation window), and the real-time IP blocklist, country blocking, reputation checks and audit-log retention are what $149–$1,250/yr actually buys. One agent read the Wordfence 9.0.1 source directly from wordpress.org SVN and mapped the architecture worth copying: the auto_prepend_file install with marker comments and chained previous prepends, file-based storage the pre-WordPress phase can read, TOTP with last-window persistence for replay protection, and the learning-mode allowlist trick. It also live-tested the free APIs that replace the paid feeds: wordpress.org core checksums and exact-version package downloads, HIBP's keyless k-anonymity range API, free-license IP-to-country data, and — the best find — Wordfence's own vulnerability feed, which is free for commercial use with attribution.
The build: 19 files. The WAF is one engine with two entry points: an auto_prepend stub that runs before WordPress (and before any dropped shell), and a plugin-mode fallback. Detection is integrity-first — wordpress.org checksums for core, exact-version package manifests for plugins/themes — with transparent heuristics scored above a threshold, an optional open GPL hash feed, and database scanning that the market leader lacks. A planned signature corpus was deliberately replaced by this integrity-first design mid-build.
Real bugs found by real tests: (1) with the prepend active, the plugin loaded the engine class a second time — fatal on every request, masked by the page cache serving stale pages; a class guard fixed it, and the lesson (a cache can hide a fatal) went straight into the test checklist. (2) The rate-limit counter file's PHP guard prefix was 14 characters but the reader skipped 15 — every request ate the JSON's first brace and reset the counter to 1. (3) Root-directory core files were queued twice under two different check types, and the second pass overwrote the "flagged" verdict with "clean", so a tampered core file escaped the second scan. (4) The login-error masking filter also masked ShieldZip's own breached-password and 2FA messages.
Verified end to end on a live install: SQLi/LFI/XSS/RCE/object-injection/enumeration requests all 403 with the correct rule id logged, while "the union started selecting members from each group" passes (two-stage SQLi confirmation); a rogue PHP file in the web root blocked with WordPress never booting; attacks on cached pages blocked before the page cache; TOTP passing all five RFC 6238 test vectors, then the full login flow — gate, wrong code, success cookie, and the same code rejected on replay; a breached password ("admintest123" — which turned out to be genuinely breached, colliding with our own test account) blocked at login with the HIBP round-trip; five failed logins locking the IP out of the login page; a 33-request 404 storm auto-blocking the client; Liechtenstein's 62 CIDR zones compiling to 61 merged binary ranges with boundary-exact binary-search hits; and the scanner catching all four planted artifacts — a tampered core file, an unknown file in wp-includes, PHP in uploads, a fake wp-config backup — plus a rogue-admin baseline diff, then repairing the core file from wordpress.org SVN (checksum-verified) and round-tripping quarantine/restore. Bonus: the scanner flagged genuinely corrupted, truncated core files that had been sitting unnoticed in our test install since an interrupted update.
Reviews
Used Free Wordfence Alternative — WordPress Security & Firewall Plugin? A star rating takes two seconds and helps others.
More builds
License: MIT — free for personal and commercial use, no warranty. Software is provided as is; review the code before running it in production (it's short enough to actually read).